Detect
AI agents examine the code for high-severity issues, including logic and access-control flaws no rule describes.
One view of what is exposed, what is still open, and what to fix next
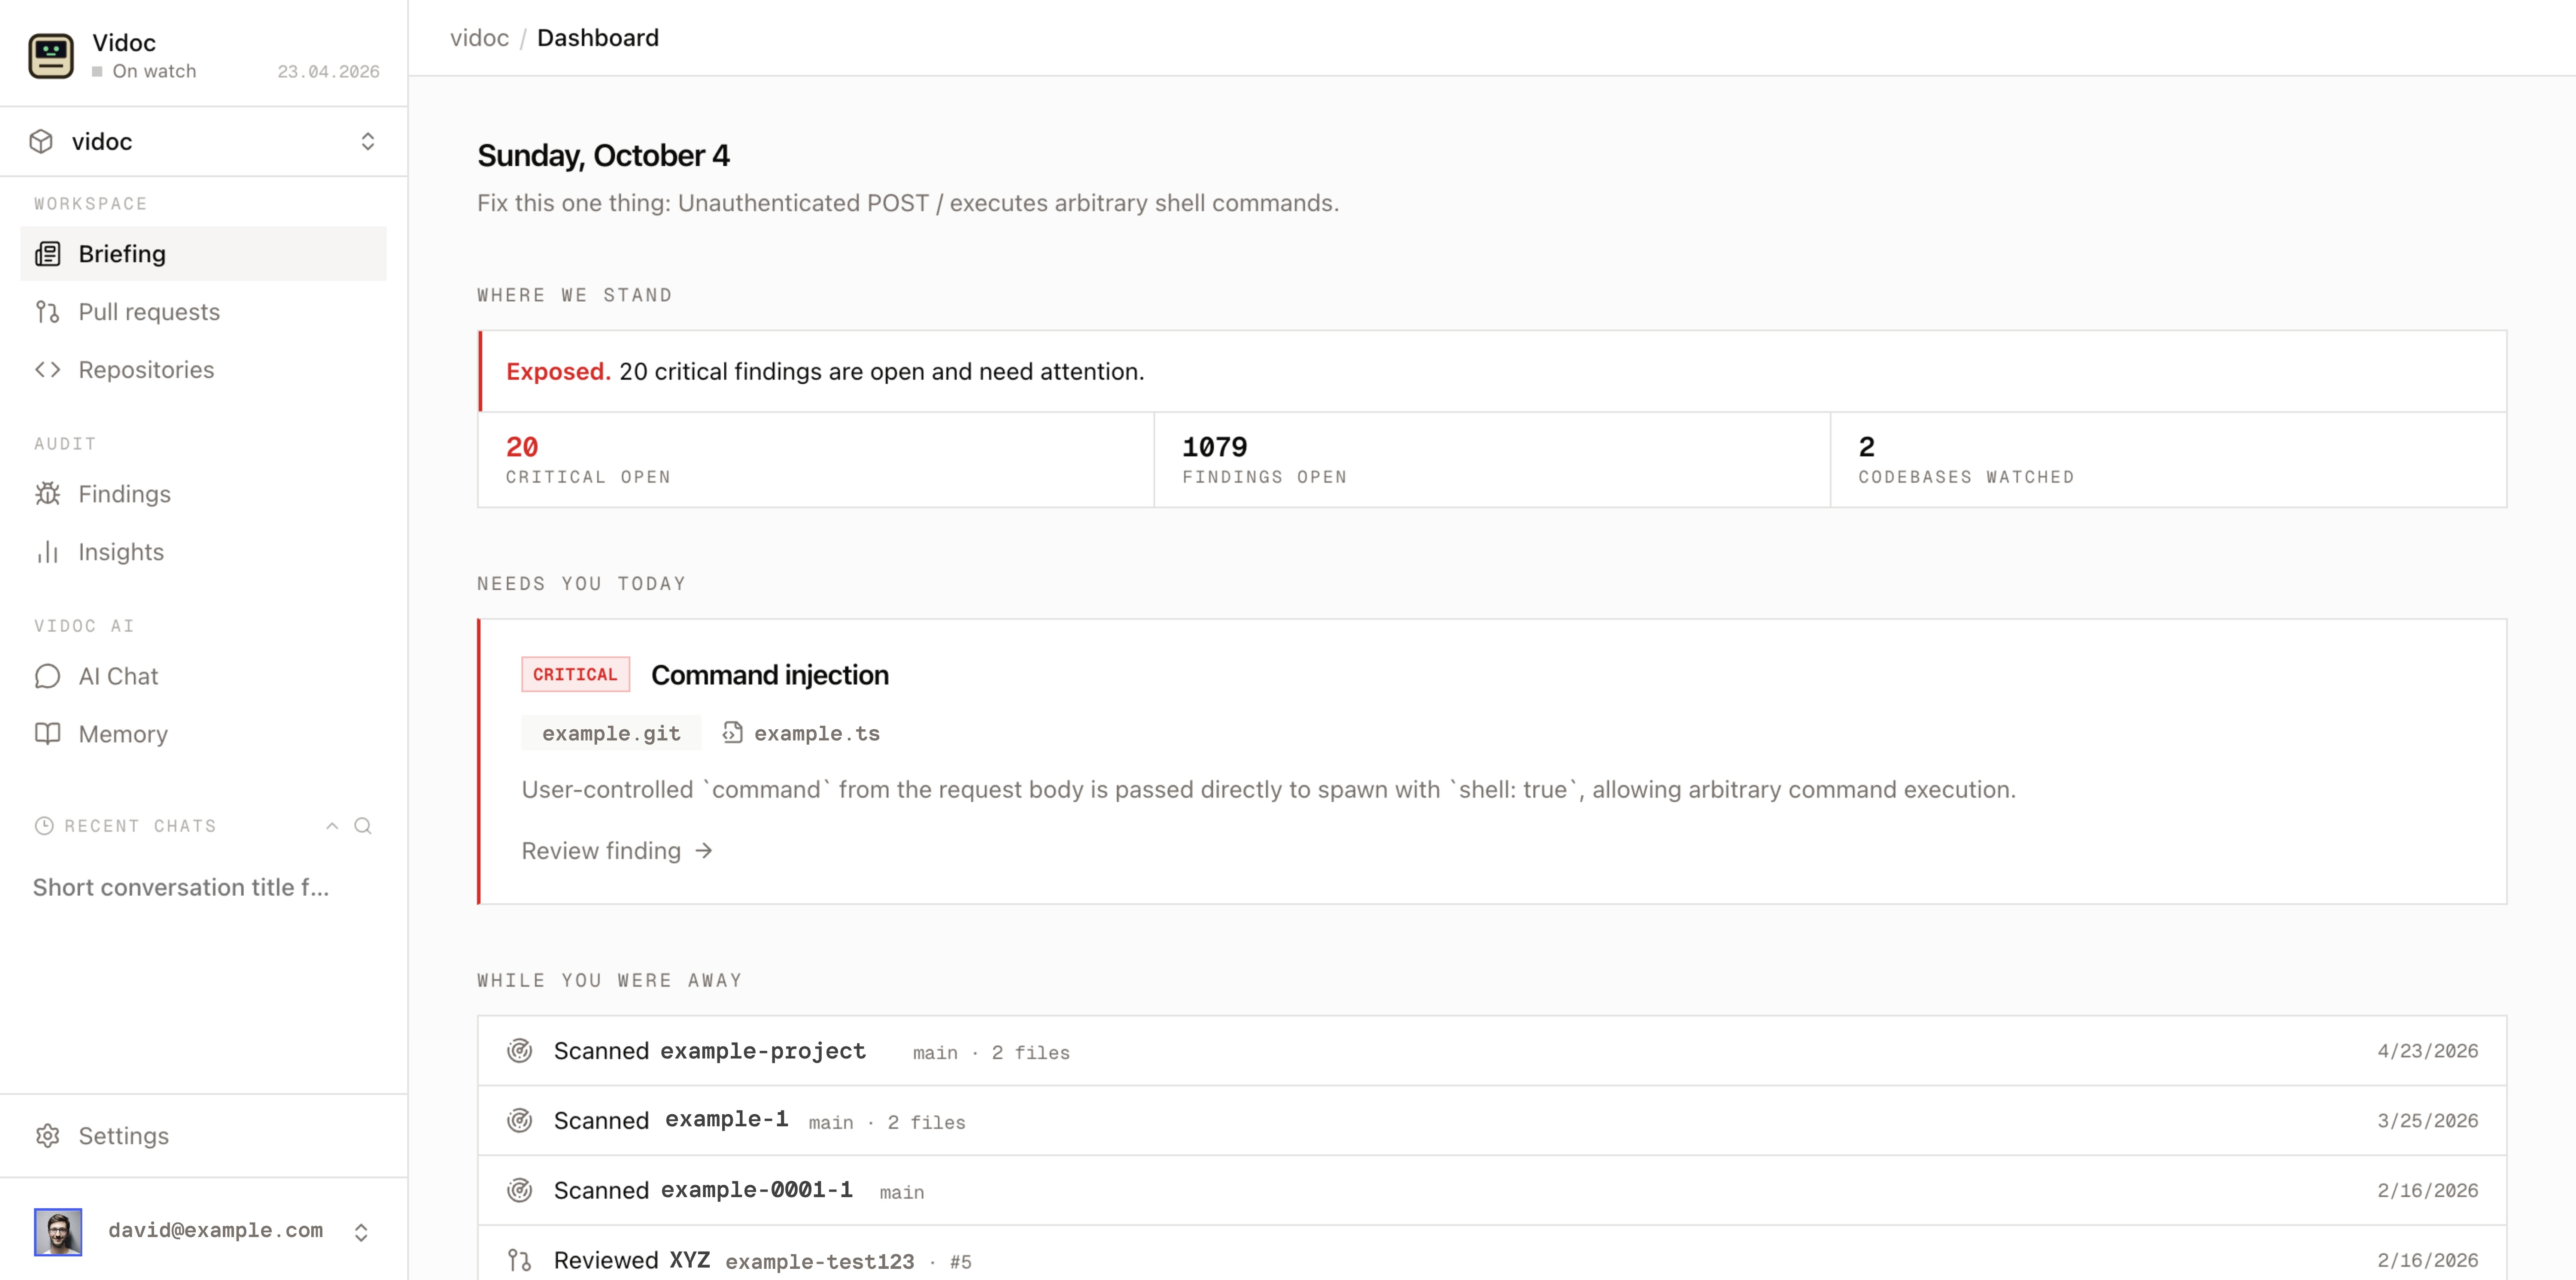
See your security status, priorities, and progress in one place. Spend less time piecing together updates and more time reducing risk
Watch videoIssues solved
186
Remediation time
− 27%5.4h
Issues by severity
VIDOC fixes
+ 14%48
Scanned pull requests
Scanned
754
With issues
61
All issues
446
Issues open
23
Critical
104
High
307
Medium
12
Low
Missing authentication
scan-test.git · main.ts:6
Command injection
scan-test.git · main.ts:9
SQL injection in search
api · search.ts:42
Open redirect via returnTo
web · auth/callback.ts:18
VIDOC follows your business logic and validates findings like a human security engineer. Spend less time reviewing false positives and more time fixing real vulnerabilities
Learn moreVIDOC Memory grows with your code over time, learning from your team's feedback on findings, PR review replies and Slack conversations
AI Security EngineerIgnore insecure account linking via email
Findings labeled as insecure ...Full learning
A closed security loop on every pull request. VIDOC identifies, verifies, and patches vulnerabilities so your team only acts on what truly matters
AI agents examine the code for high-severity issues, including logic and access-control flaws no rule describes.
Every critical and high finding is checked against your code. Only confirmed issues reach your team.
Prioritizes the issues that matter and cuts out false positives before they reach your team.
Findings land in the pull request with a proposed fix. Your team's decisions feed VIDOC's memory.
Find security issues across your application code and infrastructure configurations
 Java
 JavaScript
 TypeScript
 Python
 Go
 C
 C++
 C#
 PHP
 Kotlin
 Rust
 Swift
 Ruby
 Scala
 Dart
 Terraform
 Pulumi
 Dockerfile
 Jenkinsfile
 Kubernetes
VIDOC works inside the tools your engineers already use,
with no extra dashboard to keep track of
CI/CD
Reviews every pull request on open and on each new commit. Inline comments, check runs, commands and feedback in the thread
Merge request reviews, inline comments, commit status, commands and feedback.
Pull request reviews, inline comments and build status.
Communication
Ask VIDOC about findings in a thread and get a daily security digest in your channel.
Ask Vidoc about findings in a thread and get a daily security digest in your channel.